Is your consent scan telling the truth?
Test scanner claims against real evidence before spending developer time.

Organization
Industry
Challenge
Stack
Products / Services Used
A high-end lighting manufacturer needed to move away from a fragmented system of static templates and manual updates.
Their goal was a high-performance, public-facing platform that mirrored their Figma design system perfectly. It lets their team manage complex data without developer help. On the surface, the project looked like a standard brochure site. However, the underlying product data was incredibly complex.
Mavlers Agency built a single Craft CMS-powered platform that keeps the front end faithful to the Figma designs while giving the client's team control over day-to-day publishing.

Adaptive Twig template powering every Light Fittings product, interior and exterior
Craft Commerce product types running through one catalogue structure
New front-end templates needed to launch a future product series or capability page


Organization
Industry
Services Used
Lorem ipsum dolor sit amet, consectetur adipiscing elit. Suspendisse varius enim in eros elementum tristique. Duis cursus, mi quis viverra ornare, eros dolor interdum nulla, ut commodo diam libero vitae erat. Aenean faucibus nibh et justo cursus id rutrum lorem imperdiet. Nunc ut sem vitae risus tristique posuere.
Lorem ipsum dolor sit amet, consectetur adipiscing elit. Suspendisse varius enim in eros elementum tristique. Duis cursus, mi quis viverra ornare, eros dolor interdum nulla, ut commodo diam libero vitae erat. Aenean faucibus nibh et justo cursus id rutrum lorem imperdiet. Nunc ut sem vitae risus tristique posuere.
Lorem ipsum dolor sit amet, consectetur adipiscing elit. Suspendisse varius enim in eros elementum tristique. Duis cursus, mi quis viverra ornare, eros dolor interdum nulla, ut commodo diam libero vitae erat. Aenean faucibus nibh et justo cursus id rutrum lorem imperdiet. Nunc ut sem vitae risus tristique posuere.
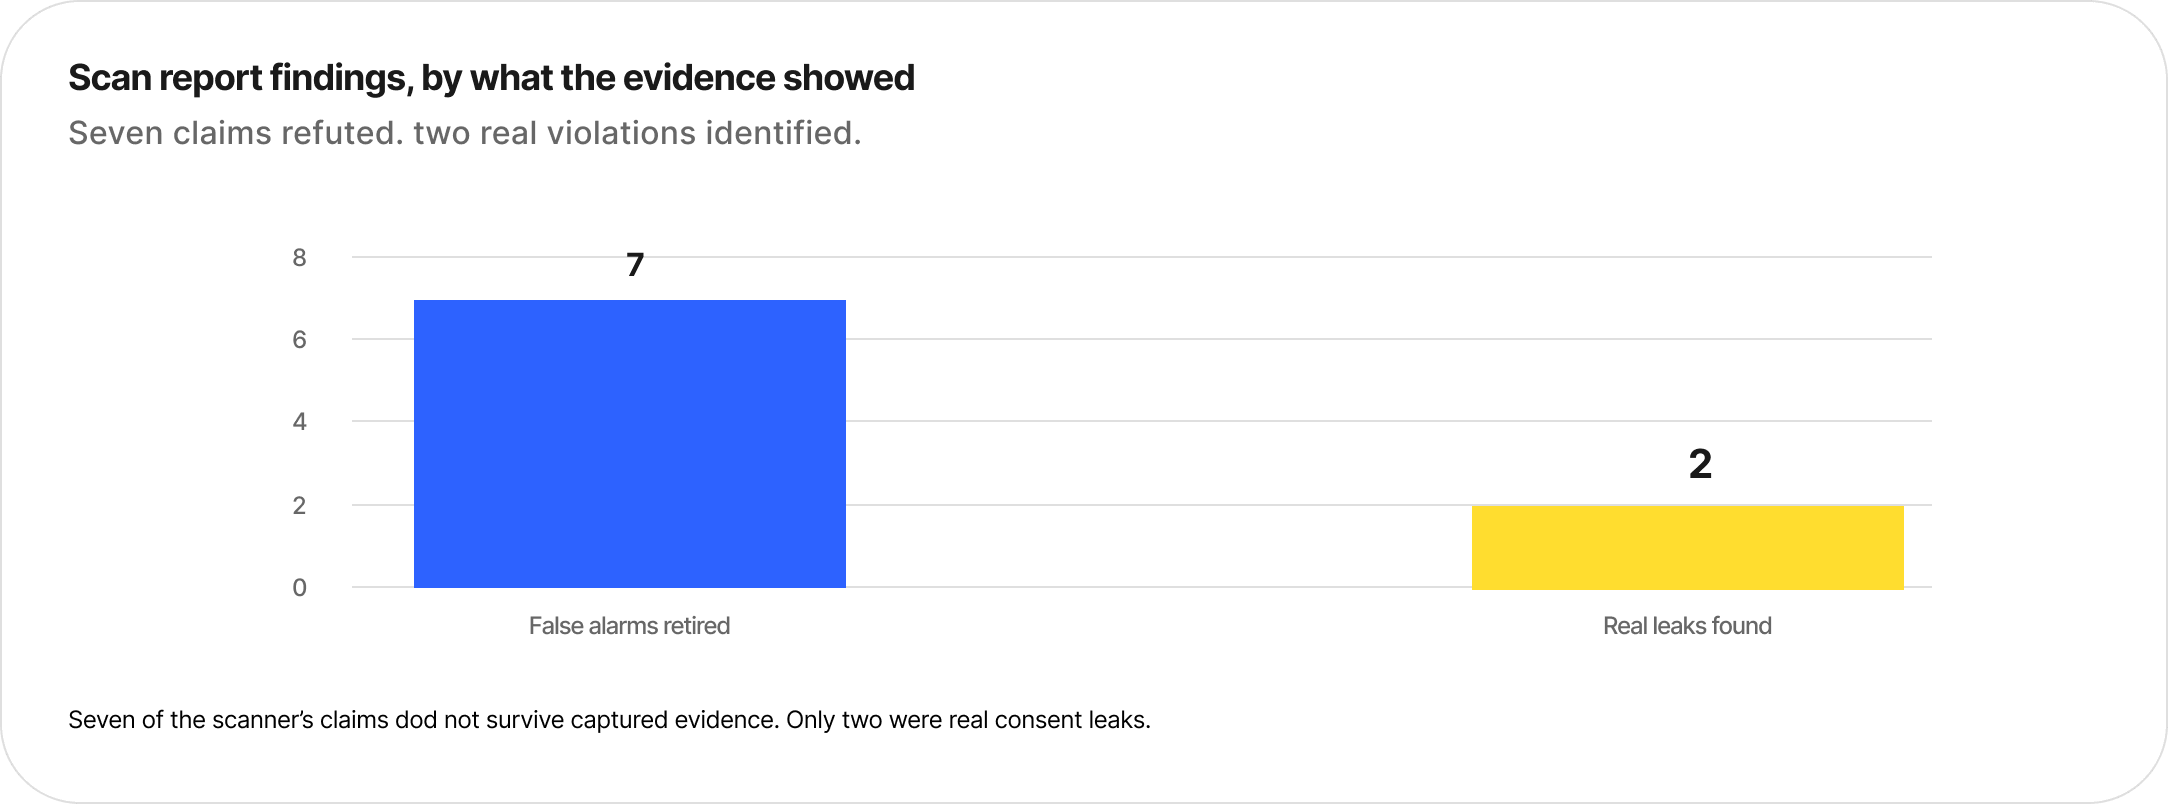
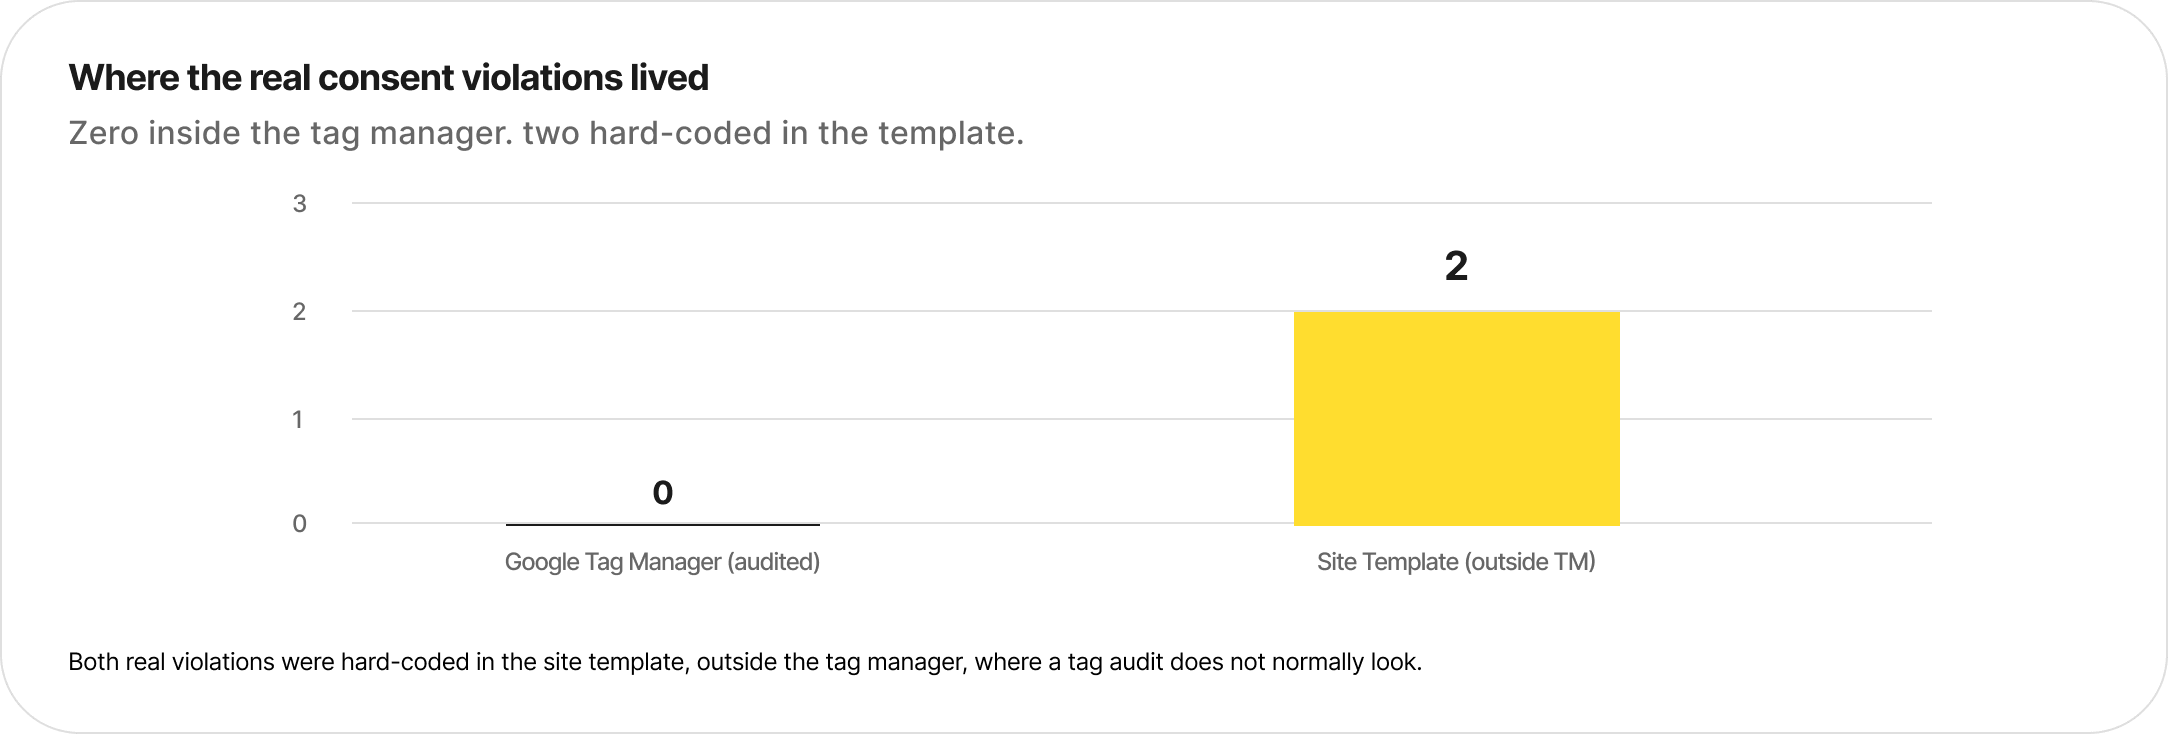
The client is a UK flooring manufacturer with residential and commercial sites, engaged through its web agency. A third-party compliance scanner issued a report listing consent-rule violations and asked the agency to act on them. Acting would have meant developer time across the site template, the tag manager, and the consent platform. Before committing the time, the agency asked for an independent audit: is the scan right, and if not, what is actually wrong?
Successful migration of 9,000+ pages across 12+ languages, with no critical downtime.
Multi-channel strategy driving 50%+ monthly registration growth.
Ogilvy needed to scale SEO delivery across multiple markets without expanding headcount. Mavlers Agency stepped in as their invisible production partner.
We'll get back to you within 4 business hours.


See how Mavlers Agency appears across AI search. Each button takes you directly to an AI search for “Mavlers Agency – White Label Digital Agency.”