

Table of contents
Get in touch
Expect response in 4 hours.
Your WordPress website can appear completely normal to you while showing visitors a fake Cloudflare verification page that tries to infect their computers.
This attack technique is known as ClickFix.
Attackers compromise legitimate websites and use fake verification pages, browser errors, or software-fix prompts to convince visitors to copy and run a malicious command. The page may look like Cloudflare. It may show a familiar “Verify you are human” message. It may use a checkbox, a spinner, and professional-looking design.
But a genuine human-verification check runs in the browser. It does not ask you to open Windows Run, PowerShell, Terminal, or any other system utility and paste a command.
If a webpage asks you to do that, close the tab immediately.
What is a ClickFix WordPress attack?
ClickFix WordPress attack is a social-engineering technique that tricks people into executing malicious commands themselves. Instead of relying only on a vulnerability or an automatic download, the attacker creates a believable problem and offers a “quick fix.”
A ClickFix malware compromises a WordPress site and uses it to display a deceptive browser prompt.
The page tells visitors that they must complete an extra step to access the website. That step usually involves opening a trusted operating-system tool and pasting a command.
The technique is dangerous because the visitor is persuaded to execute the attacker’s code through a legitimate tool already present on the computer.
How a fake Cloudflare verification works
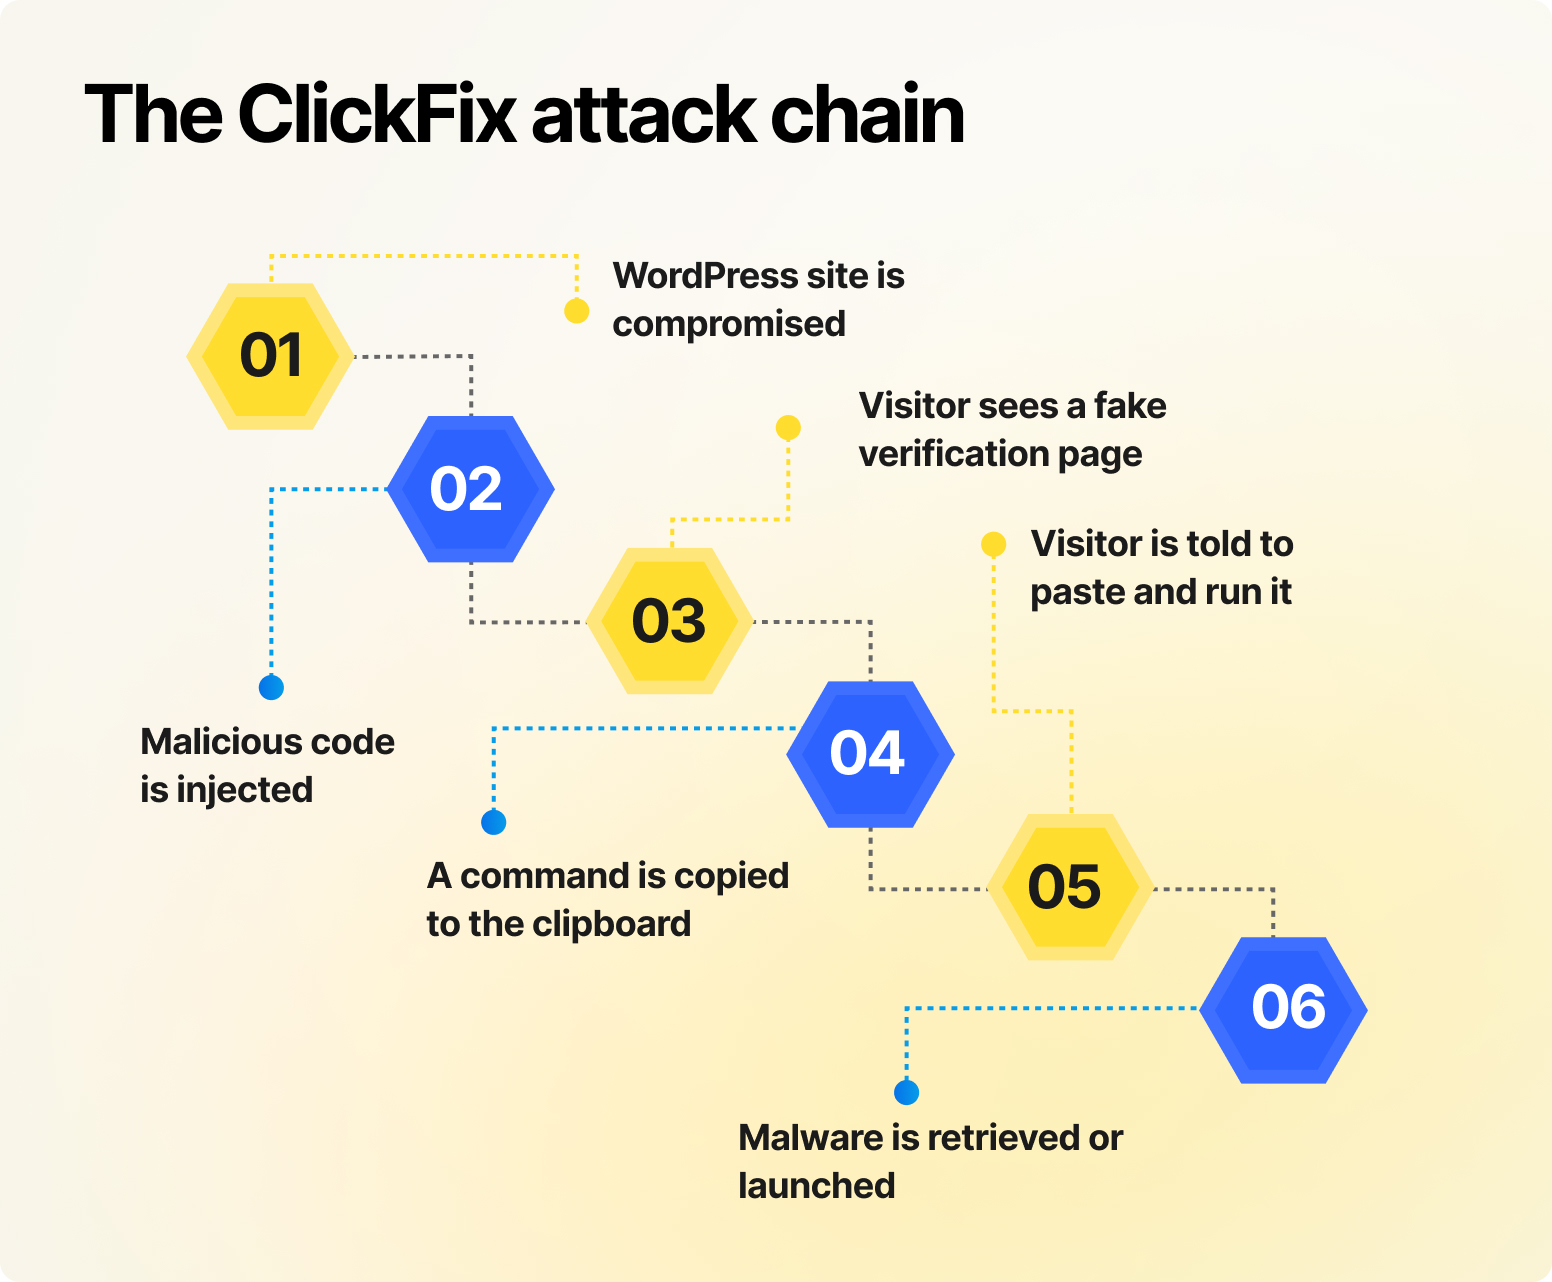
Although individual campaigns vary, a typical ClickFix attack follows this sequence:
- The attacker compromises a website. An outdated plugin, stolen credential, vulnerable theme, or malicious extension may provide access.
- Malicious code is injected. The code may alter a theme file, plugin, database entry, scheduled task, or server configuration.
- A visitor sees a fake verification page. The page may imitate Cloudflare Turnstile, reCAPTCHA, or another familiar service.
- The page writes a command to the clipboard. This can occur when the visitor clicks a verification element.
- The visitor is told to paste and run it. Common instructions include opening Run, PowerShell, Command Prompt, File Explorer, or Terminal.
- The command retrieves or launches malware. The final payload can vary by campaign.
Possible payloads include information stealers, remote-access tools, loaders, and other malicious programs. These may expose saved passwords, session cookies, crypto wallets, files, business credentials, and access to connected services.
What can ClickFix malware do?
The final payload depends on the campaign, but common outcomes include:
- Stealing browser passwords.
- Capturing cookies and active login sessions.
- Accessing cryptocurrency wallets.
- Downloading additional malware.
- Installing a remote-access tool.
- Establishing persistence.
- Disabling or evading security software.
- Accessing local files.
- Supporting lateral movement inside a business network.
Why WordPress site owners may not see the fake CAPTCHA
One of the most confusing features of a ClickFix WordPress compromise is selective delivery. The malicious code may show the lure only to certain visitors. It may exclude:
- Logged-in WordPress administrators
- Search-engine crawlers
- Known security scanners
- Mobile devices
- Visitors from specific countries
- Repeat visitors
- Browsers without a matching operating system
As a result, you may open the site on your phone or while logged into WordPress and see the normal homepage. Meanwhile, a customer on a Windows computer may see a fake Cloudflare CAPTCHA.
How to check what visitors see
Test the website:
1. On a Windows device
2. While logged out of WordPress
3. In a private or incognito window
4. With plugin, server, and CDN caches considered
5. Across several pages and traffic-entry points
Do not repeatedly interact with a suspected fake verification. Preserve evidence and begin containment.
How to tell whether a Cloudflare verification is fake
A genuine browser verification should remain inside the browser. Treat the page as malicious if it asks you to:
- Press Windows + R
- Open PowerShell, Command Prompt, or Terminal
- Paste clipboard content
- Run a command to prove you are human
- Disable antivirus or browser protection
- Download an unknown “verification” file
- Open File Explorer and paste text into its address bar
Other warning signs can include unusual grammar, urgent countdowns, unexpected full-screen overlays, repeated redirects, or a verification prompt appearing on a page that does not normally use one.
However, visual quality is not a reliable test. A fake page can closely imitate a legitimate brand. The decisive warning is the request to leave the browser and execute a command.
How WordPress websites become infected
A WordPress website hacked by ClickFix operators may have been compromised through one or more of these routes.
1. Outdated plugins, themes, or WordPress core
Known vulnerabilities are frequently patched by vendors. A website that misses updates can remain exposed long after a fix is available.
2. Expired or inactive premium licences
A premium plugin or theme may remain installed and functional after its licence expires, but stop receiving updates. The site can look healthy while the software becomes increasingly vulnerable.
3. Nulled themes and plugins
Cracked premium software may contain hidden backdoors or modified code. It also lacks a trustworthy update path. Remove nulled software rather than attempting to sanitize it.
4. Weak or reused passwords
An administrator, hosting, FTP, or SSH password reused elsewhere may already be available to attackers after an unrelated breach.
5. Compromised hosting or developer access
The attacker may enter through a hosting account, deployment key, abandoned administrator account, infected developer device, or another site sharing the same hosting environment.
How to clean a hacked WordPress site affected by ClickFix
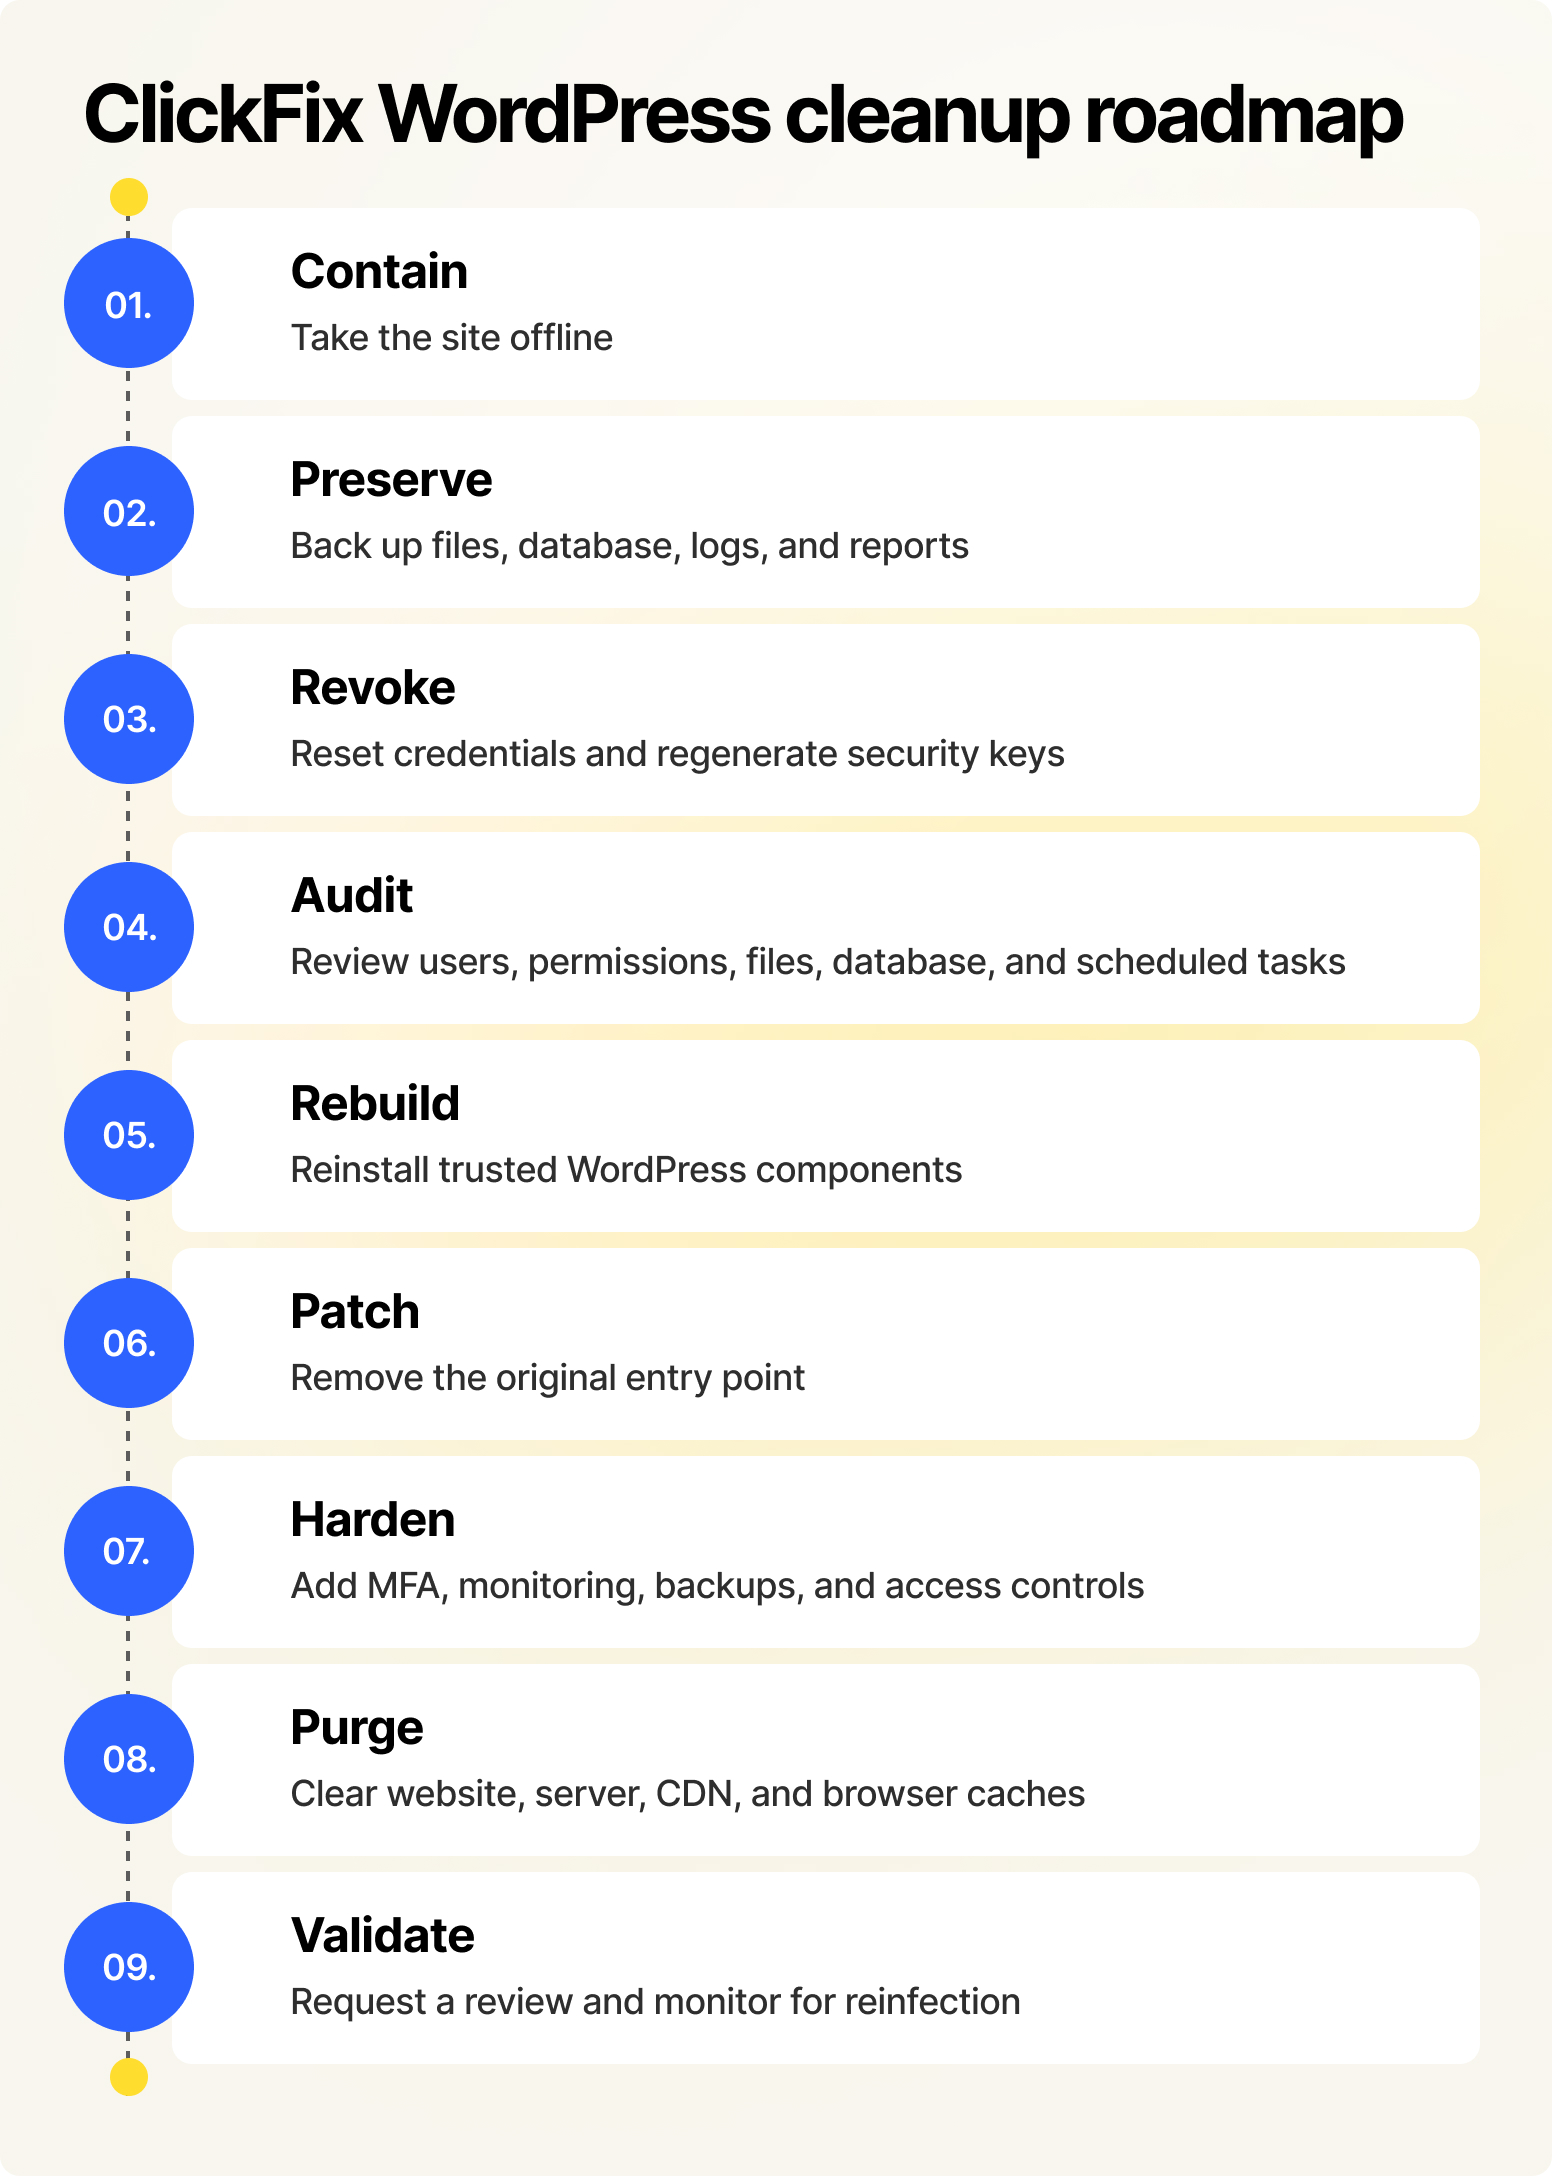
WordPress malware removal should address both the visible injection and the attacker’s persistence. Deleting one suspicious script is rarely enough.
1. Take the website offline
Put the site into maintenance mode or display a temporary holding page.
This reduces the chance of exposing additional visitors while you investigate.
Notify your hosting provider. The host may have access to server logs, malware scanners, backups, and account-level evidence that is not available inside WordPress.
2. Create a complete backup
Before changing the site, preserve a copy of:
- WordPress files.
- The database.
- Server logs, if available.
- Configuration files.
- Existing security-plugin reports.
The backup is for investigation and recovery. Do not restore it without checking it first.
3. Reset all credentials
Change every potentially exposed credential, including:
- WordPress administrator passwords.
- Hosting-panel passwords.
- FTP, SFTP, and SSH passwords.
- Database credentials.
- CDN and DNS credentials.
- Email accounts connected to website administration.
Regenerate WordPress authentication keys and salts. This invalidates existing login sessions and helps remove an attacker who is still logged in.
4. Review users and permissions
Look for administrator accounts that nobody recognizes.
Review known accounts as well. An attacker may have changed the email address, password, role, or recovery details of a legitimate user.
Reduce privileges wherever possible. Most content contributors do not need administrator access.
5. Inspect high-risk locations
Pay close attention to:
- header.php
- footer.php
- functions.php
- wp-config.php
- .htaccess
- wp-content/mu-plugins
- wp-content/uploads
- Theme and plugin directories.
- The WordPress database.
- WP-Cron events.
- Server-level scheduled tasks.
PHP files in the uploads directory deserve particular scrutiny because that directory normally stores media rather than executable application code.
Also search the database for injected scripts, suspicious redirects, unfamiliar domains, and modified options or posts.
6. Reinstall trusted files
For a reliable cleanup, reinstall:
- WordPress core.
- Plugins from official or verified sources.
- The parent theme.
- Premium themes and plugins obtained from valid vendors.
Keep only files that have been inspected and are genuinely needed. Review uploads and child themes carefully before restoring them.
If multiple sites share the same hosting account, investigate all of them.
7. Remove the original entry point
A cleanup is incomplete if the vulnerability remains open.
Update WordPress, themes, and plugins. Remove abandoned software and uninstall anything you do not use.
Delete all nulled or cracked plugins and themes. Replacing them with licensed or reputable alternatives is part of the cleanup—not an optional extra.
8. Harden access
Add safeguards such as:
Disable the built-in file editor by adding this line to wp-config.php: define('DISALLOW_FILE_EDIT', true);
Have a qualified WordPress or security professional review configuration changes before deploying them to a production website.
9. Clear caches and request a review
Clear:
- WordPress caching-plugin data.
- Server-side caches.
- CDN caches.
- Browser caches, where relevant.
A stale cached response can continue serving the fake page after the source files have been cleaned.
If Google has flagged the site, review the issue in Google Search Console and request a security review after confirming that the compromise has been removed.
Continue monitoring the website after cleanup. If the fake Cloudflare page returns, a backdoor, hidden account, scheduled task, or database injection may still be present.
What to do if you ran the fake verification command
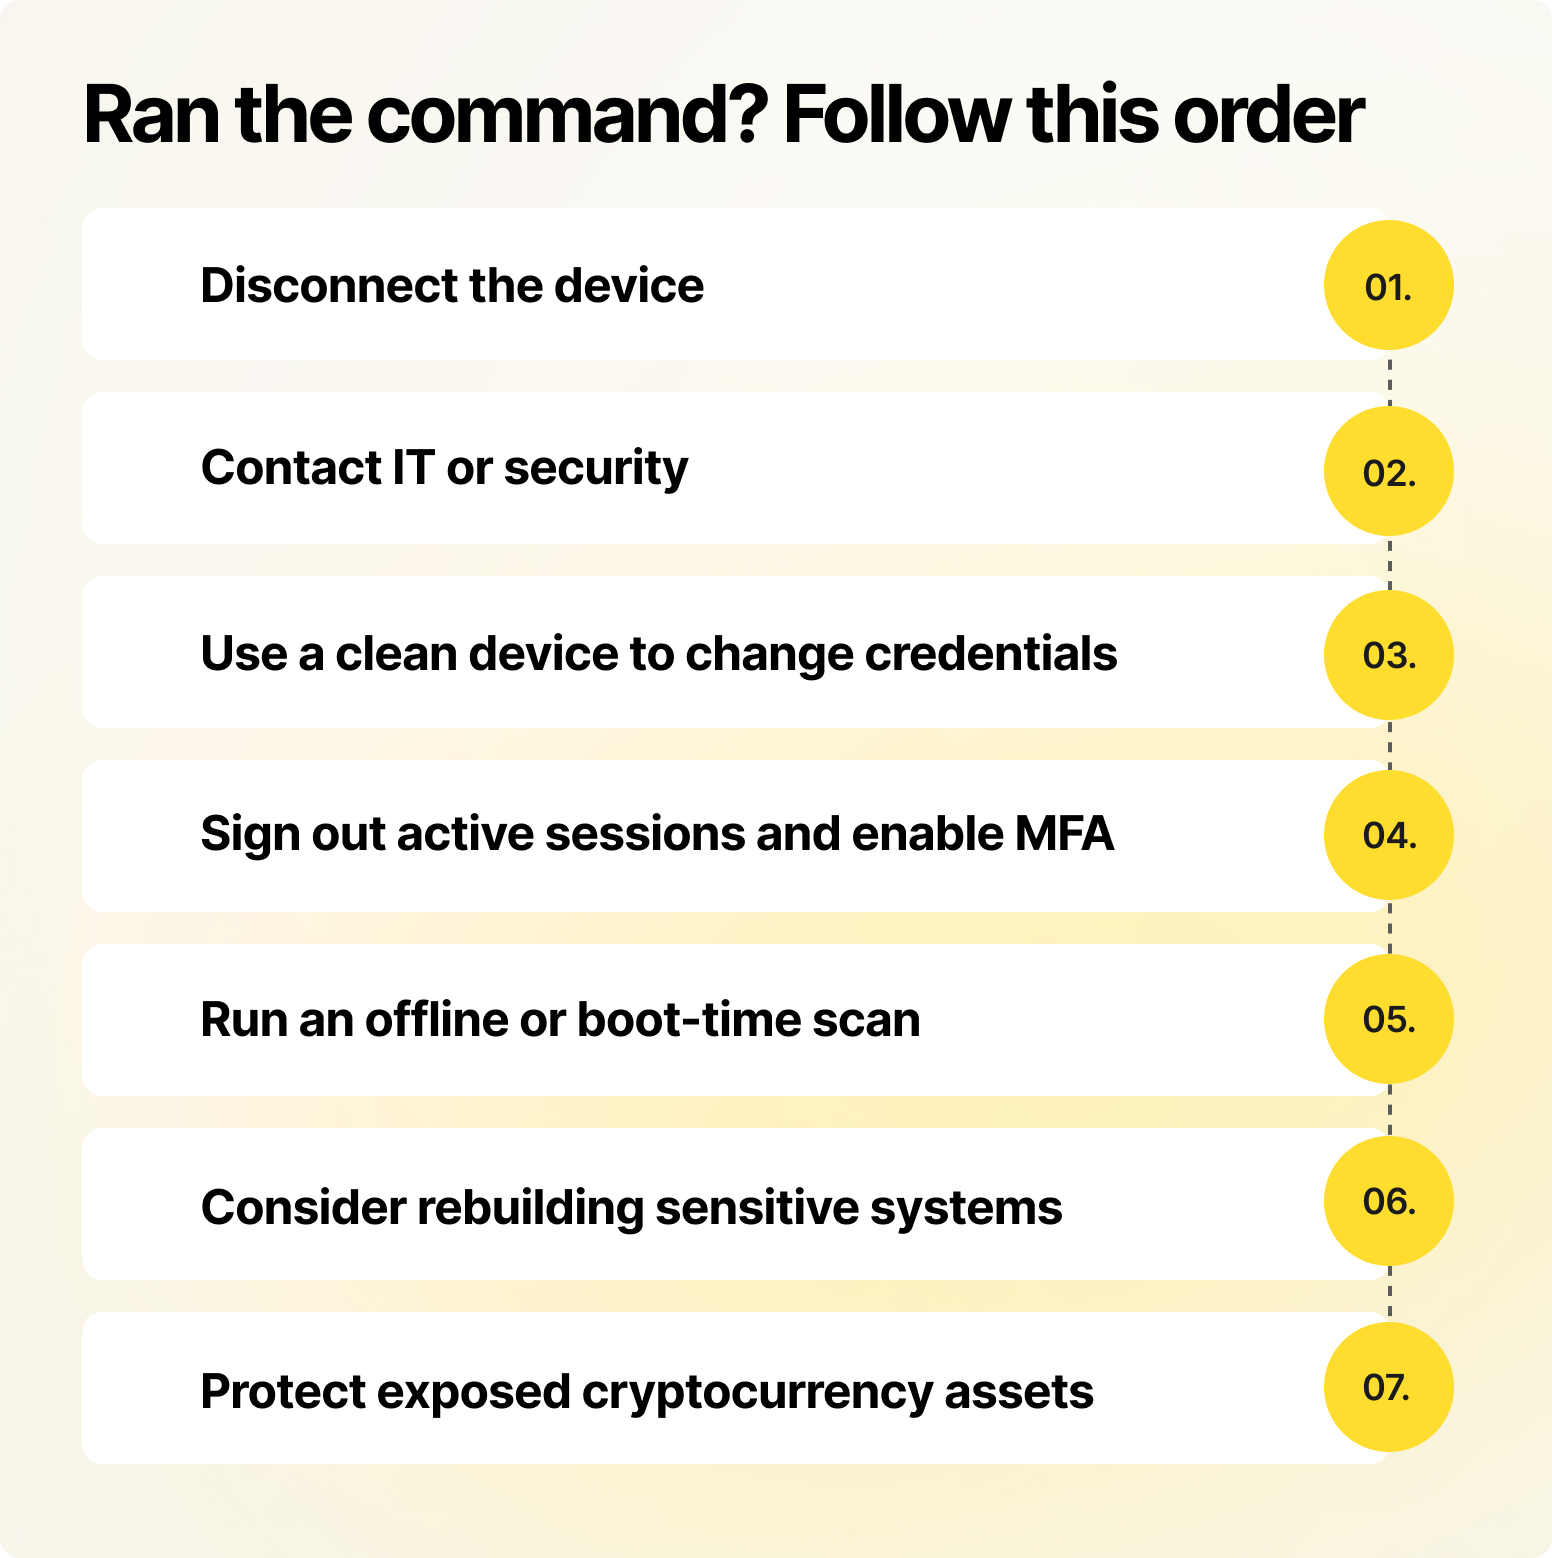
If you pressed the keys and executed the command, assume the device and browser sessions may be compromised - even if nothing visible happened.
1. Disconnect the device
Turn off Wi-Fi and unplug the network cable. Closing the browser or terminal does not undo the command.
2. Contact IT or security
If the device is used for work, report the incident immediately. Stolen sessions or credentials can expose email, cloud tools, code repositories, customer systems, and internal applications.
3. Change credentials from a clean device
Start with the primary email account because it can reset many other accounts. Then update:
- Banking and payment accounts
- Work accounts
- Password managers
- Cloud storage
- Social accounts
- Developer and hosting services
Use “sign out of all sessions” or equivalent controls. Enable phishing-resistant multi-factor authentication where available.
4. Scan - and consider rebuilding - the computer
Run a reputable offline or boot-time scan. A clean result does not guarantee that credentials or sessions were not already stolen.
For systems used for sensitive business, financial, or administrative work, rebuilding the operating system from trusted media may be the safer recovery option. Coordinate with your IT team before wiping a corporate device so evidence can be preserved.
5. Protect cryptocurrency assets
If wallets or seed phrases may have been accessible, create a new wallet on a clean device and transfer assets according to appropriate security procedures. Merely changing a password may not protect a compromised wallet.
How to prevent future ClickFix WordPress infections
Effective ClickFix prevention requires controls at the website, user, and endpoint levels.
For WordPress owners
- Maintain a complete plugin and theme inventory
- Remove unused software
- Apply security updates promptly
- Verify premium licences
- Never use nulled themes or plugins
- Require multi-factor authentication
- Keep tested off-site backups
- Monitor file and database changes
- Review scheduled tasks and administrator accounts
- Separate sites and hosting privileges where practical
- Use a managed WordPress or security partner when internal coverage is limited
For organizations and employees
Train users around one behavior:
Never paste a command into an operating-system tool because a webpage told you to.
Security teams can also monitor suspicious chains involving browsers, Explorer, PowerShell, script hosts, download utilities, and unusual outbound connections. Where business operations permit, restrict unnecessary script execution and access to system tools commonly abused by these campaigns.
Frequently asked questions
Does Cloudflare ever ask users to open Run or Terminal?
No legitimate Cloudflare human-verification flow should ask a visitor to open the Windows Run dialog, PowerShell, Command Prompt, File Explorer, or Terminal and paste a command.
Is my site safe if I cannot see the fake Cloudflare verification?
Not necessarily. Malicious code may hide from logged-in administrators, mobile users, crawlers, scanners, or particular locations. Test while logged out and investigate the site at the file, database, user, scheduled-task, and hosting levels.
Can a WordPress security plugin remove ClickFix malware?
A security plugin can help identify modified or suspicious files, but it may not detect every database injection, cron job, hidden account, server-level change, or stolen credential. Treat automated scanning as one part of a broader incident response.
Why does the fake CAPTCHA keep returning?
Persistent reinfection means the cleanup missed a backdoor, scheduled task, database entry, hidden administrator, vulnerable component, compromised credential, or another infected site on the same hosting account.
Are nulled WordPress plugins and themes safe after scanning?
They should not be considered trustworthy. Their code and update chain cannot be reliably verified. Replace them with licensed software or reputable alternatives from official sources.